How AI Sandboxes Work for Safe Model Testing
A rapid implementation of AI technology can help companies achieve optimization and learn valuable insights from information. However, the employment of machine learning models without any validation carries within itself a number of risks like data leakage, bias, and prompt injections.
The application of an AI sandbox makes sure that the algorithm undergoes testing and corrections of the possible vulnerabilities prior to deployment.
The inclusion of the box in the software development life cycle makes it possible for the security team to test cyber attacks, comply with regulations, and fine-tune the accuracy of results without interrupting operations of core databases and customer systems.
What is an AI Sandbox?
Whereas the traditional software sandbox is focused on analyzing standalone malware or executing code safely, the sandbox is specifically built for evaluating the unique non-deterministic nature of machine learning models.
The AI sandbox is a kind of digital testing area that comes complete with synthetic data, security measures, and telemetry. The developers are able to check how the algorithm behaves in difficult conditions without putting their company’s proprietary databases at risk.
Differences Between Traditional & AI Sandbox Testing:
The reason why normal testing methods do not work with artificial intelligence comes down to how machine learning algorithms work:
- Targeted Approach
The conventional method tests binaries, scripts, or network traffic individually. Sandbox checks out the model weights, prompt inputs, API data flows, and behaviors.
- Threat landscape
The normal environment checks for memory buffer overflows and unauthorized changes to files. The AI testing environment checks for algorithmic drift, data extraction, model poisoning, and hallucination ratios.
- Data Requirements
The traditional methods use dummy files to run the script. The sandbox uses a wide range of anonymous synthetic data sets.
Primary Uses of an AI Sandbox Environment
The following three aspects are protected by deploying a testing environment:
1. Adversarial Security Testing
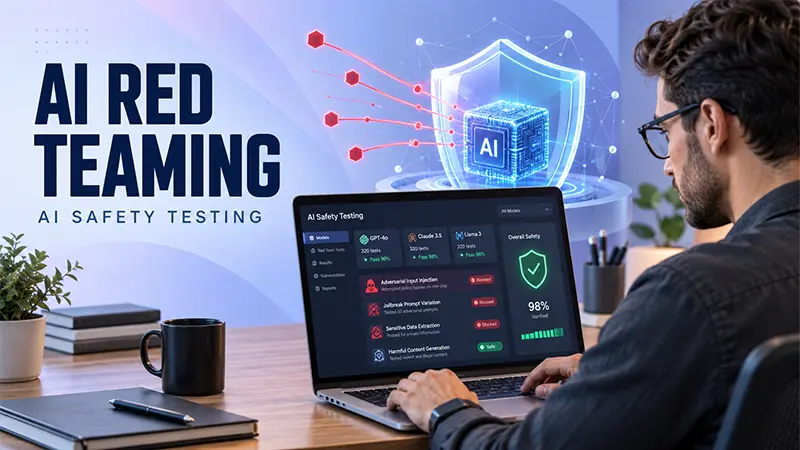
Crews conduct adversarial security testing by simulating attacks in a safe environment. This helps developers create defense filters and prompts for the system by subjecting it to prompt injections, indirect jailbreaks, and data extraction attacks.
2. Compliance and Ethics Auditing
With global compliance frameworks such as the EU AI Act, the need for auditing algorithms increases. A sandbox becomes a testbed where compliance officers can assess algorithmic bias, privacy guards, and the explainability level of the algorithms.
3. Performance and Hallucination Monitoring
Automated systems may generate confident outputs that are wrong. Testing the system in the sandbox helps to ensure that the thresholds for hallucination of the model will be maintained when the application works under heavy loads.
Best Practices for Establishing the Enterprise AI Sandbox
Establishing a test environment involves finding the right balance between ensuring a high level of security and convenience for developers:
- Synthetic and Anonymized Data
Do not employ live customer PII data to test the model, but generate synthetic data profiles in real-time as fast as the production environment operates to stay fully compliant with privacy regulations without compromising the data structure for testing.
- Network Egress Filtering
Block all API connections from the outside into the test pod to make sure that the model does not have an opportunity to leak the context of its evaluations and connect to any unauthorized websites.
- Automated Adversarial Testing
Automate security scans of the model by running adversarial prompts against model checkpoints through the CI/CD pipeline before the code reaches the production environment.
- Role-Based Access Control
Keep the number of people who can control the sandbox, export model weights, and evaluate model policies limited.
Conclusion
Launching an AI sandbox allows organizations to safely build the bridge between experimenting with new ideas and the security of their operations.
By isolating test workloads, conducting adversarial testing, and making sure of compliance within the protected environment, organizations get an opportunity to launch their intelligent solutions safely.
Frequently Asked Questions
Ans: Testing, stress-testing, and evaluating the AI model in a controlled environment.
Ans: The use of anonymized and synthetic datasets instead of live customer data.
Ans: AI models require specialized testing for bias, hallucinations, and prompts.